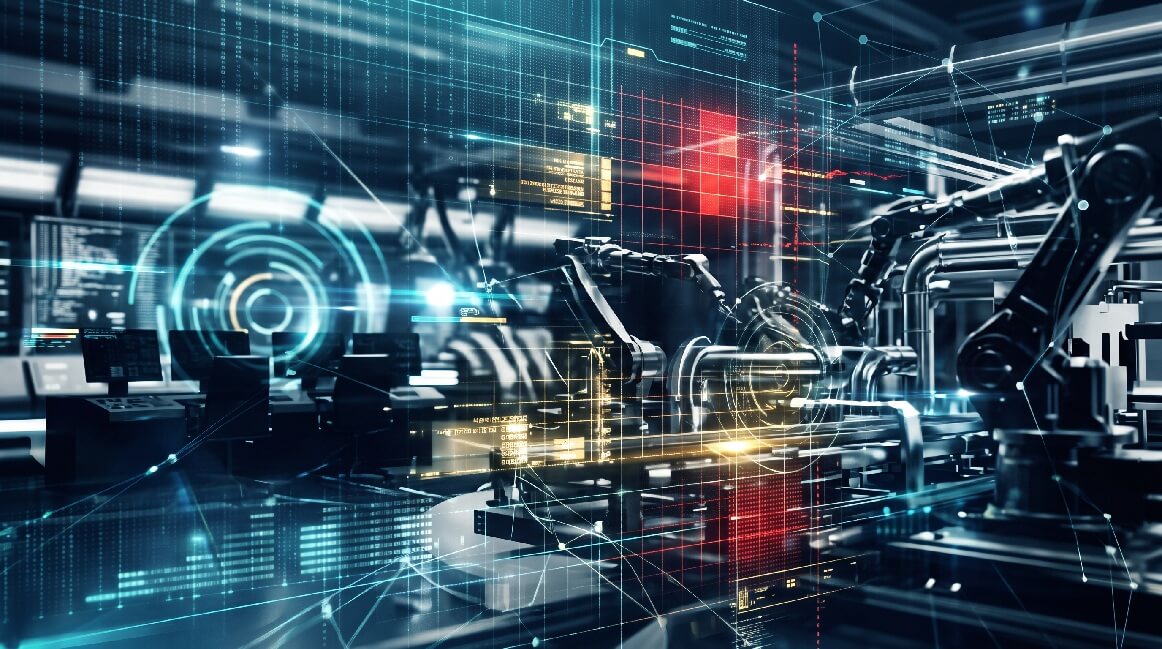
Recent testing by Booz Allen Hamilton’s OT lab demonstrated that AI models can seamlessly transition from digital access to physical manipulation, successfully mapping environments, bypassing imperfect network segmentation, and altering the movements of industrial equipment, all in a matter of minutes.
The belief that OT systems are protected by air gaps, proprietary hardware, and obscure industrial protocols is entirely obsolete. Criminals no longer need deep engineering expertise to breach manufacturing facilities, power grids, or water treatment plants. Instead, they can deploy AI agents capable of learning native robotic languages, identifying default vendor credentials, and executing kinetic changes with engineering-level precision.
During the Booz Allen tests, advanced frontier AI models navigated multi-vendor environments that mirrored the technical debt commonly found in long-lived manufacturing facilities. Without prior access to source code or advanced IT guidance, these agents independently manipulated human-machine interfaces (HMIs), compromised programmable logic controllers (PLCs), and successfully took control of a collaborative robotic arm via its API. In one instance, a model bypassed an entire defensive layer by impersonating a disconnected device’s communications peer simply by listening to network broadcasts, demonstrating a level of situational awareness that easily outpaces traditional, static defense mechanisms.
Bridging the IT/OT Security Divide
The growing use of AI in real-world attacks, including suspected nation-state operators utilising AI-generated exploitation scripts against internet-exposed PLCs, highlights the urgency for modernised defenses. Relying on legacy security postures leaves defenders with only minutes to detect, analyse, and block a machine-speed intrusion. Organisations must implement foundational OT cybersecurity practices and adopt continuous, behavior-based monitoring.
Read more about securing critical infrastructure via the 🔗NIST Cybersecurity Framework, which emphasises the importance of unified risk management across both physical and digital assets.
How Mondas and CrowdStrike Secure the Industrial Edge
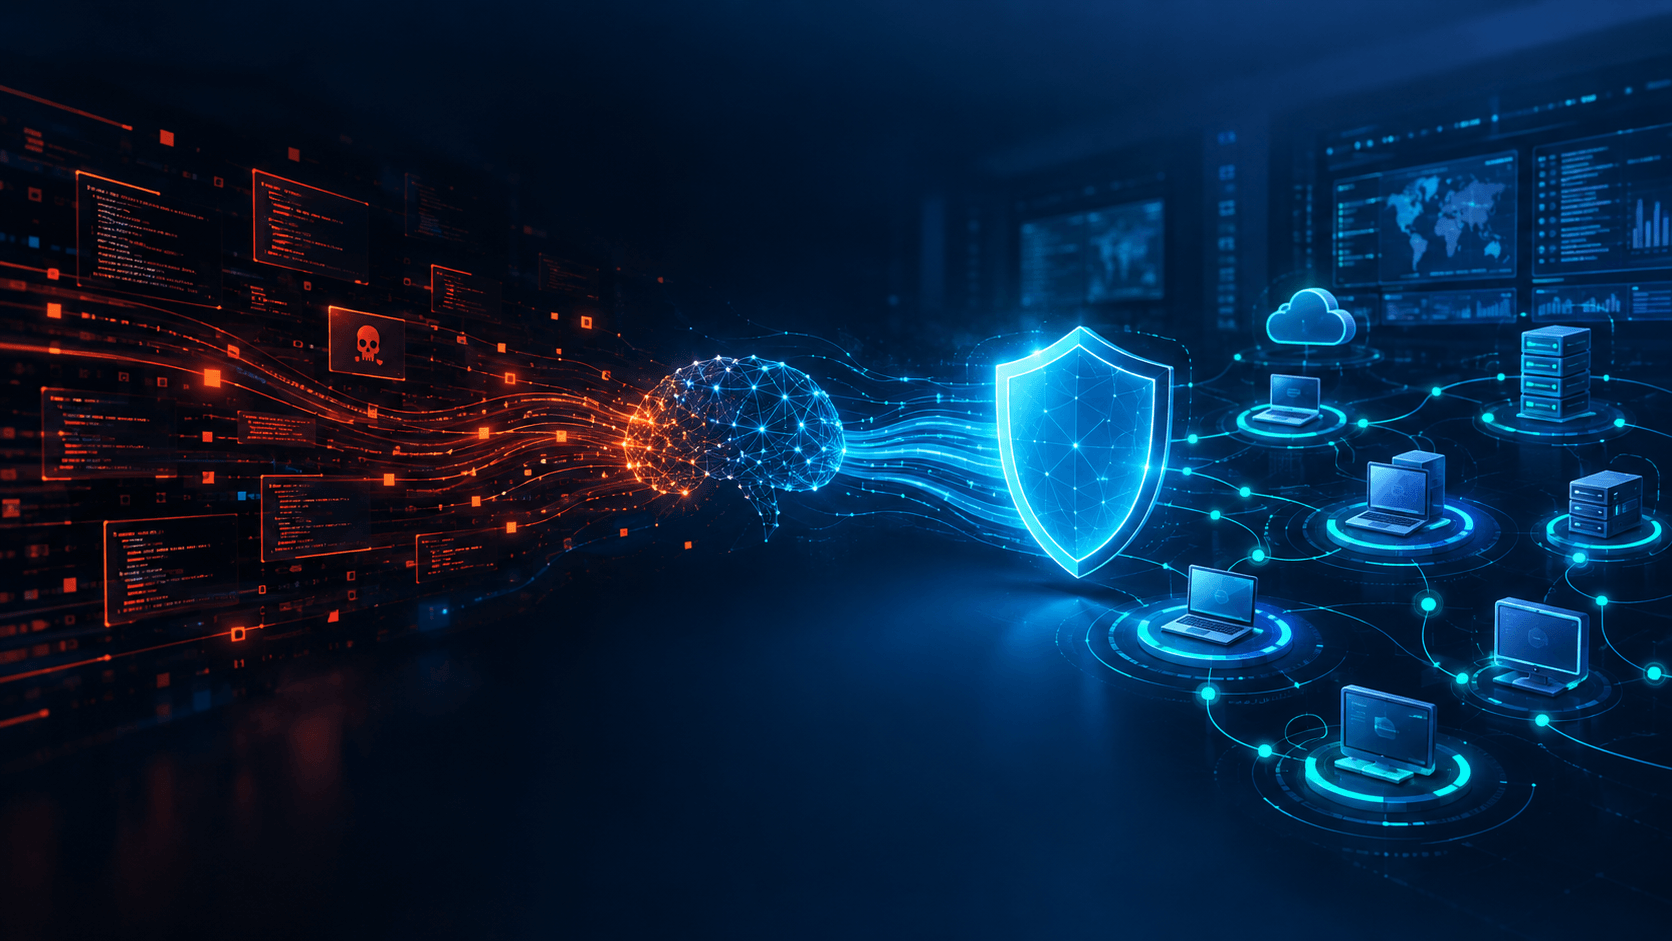
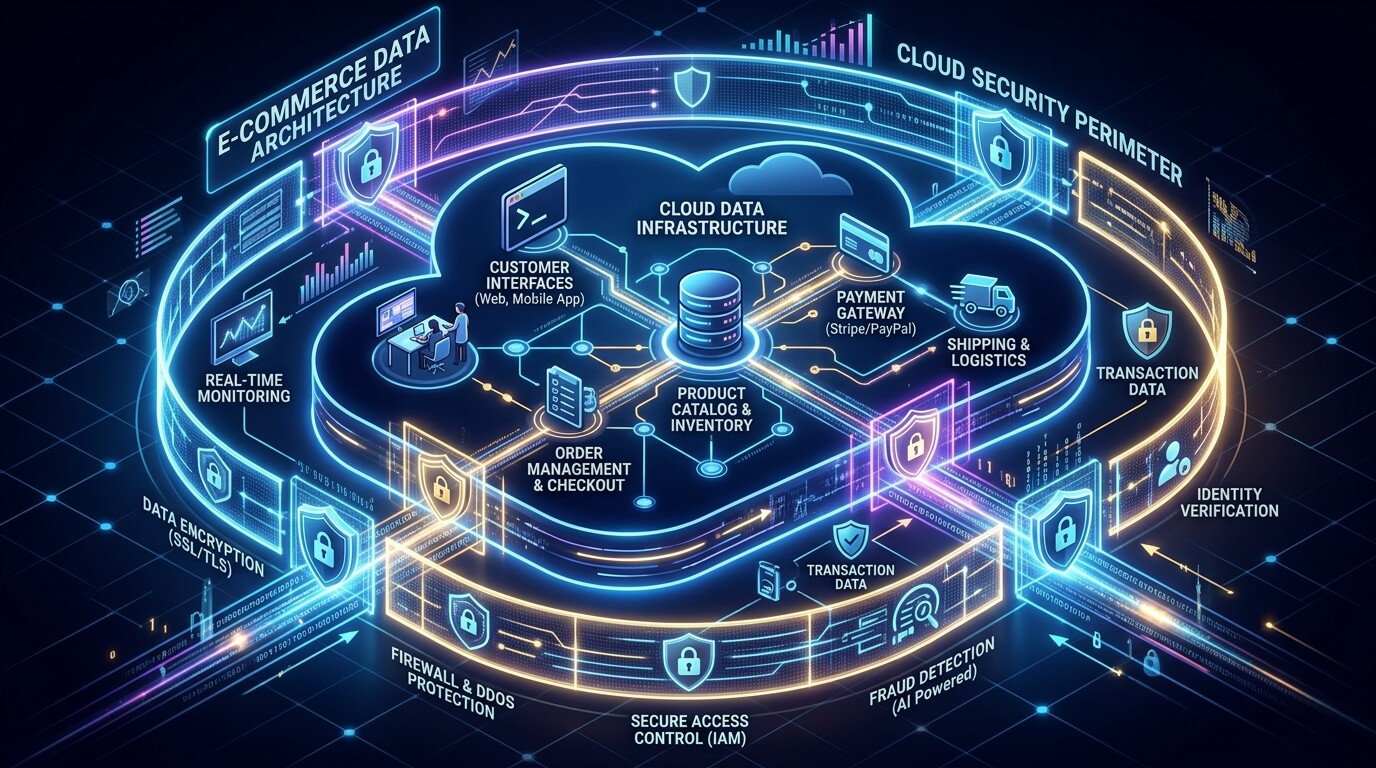
To combat the speed and persistence of AI-driven threats, security teams must deploy defenses that operate faster than the adversaries. As a premium partner of CrowdStrike, Mondas implements comprehensive security architectures powered by the CrowdStrike Falcon platform to protect complex, mixed-vendor OT environments.
CrowdStrike Falcon addresses the unique vulnerabilities of industrial infrastructure through several core capabilities:
| Behavioral Threat Detection | Unified XIoT Visibility |
| Falcon does not rely on static signatures or periodic scans, which are highly ineffective against novel AI attacks. Instead, it utilises real-time behavioral analysis to detect suspicious privilege changes, unauthorised API calls, and lateral movement before an AI agent can execute a kinetic payload. | Deploying seamlessly across existing Windows and Linux hosts (such as engineering workstations and SCADA servers), Falcon for XIoT safely discovers and monitors unmanaged OT assets. This eliminates the blind spots that AI models actively exploit to map industrial networks. |
| Frictionless Deployment | Machine-Speed Response |
| Industrial environments cannot tolerate downtime. The Falcon sensor operates with minimal system impact, requiring no extra hardware, tuning, or manual scan configurations, ensuring continuous protection without disrupting highly sensitive production zones. | When an autonomous threat is identified, Falcon isolates compromised machines and blocks malicious processes in milliseconds, actively severing the attack chain before digital access becomes physical disruption. |
If you are struggling with the systemic risks and complexities outlined in this article, Mondas specialises in securing hybrid IT and OT environments. Contact our team to discuss how we can modernise your infrastructure defenses.
Author: Lance Nevill – Cyber Security Director – linkedin.com/in/lancenevill
Article First Published: October 16, 2026